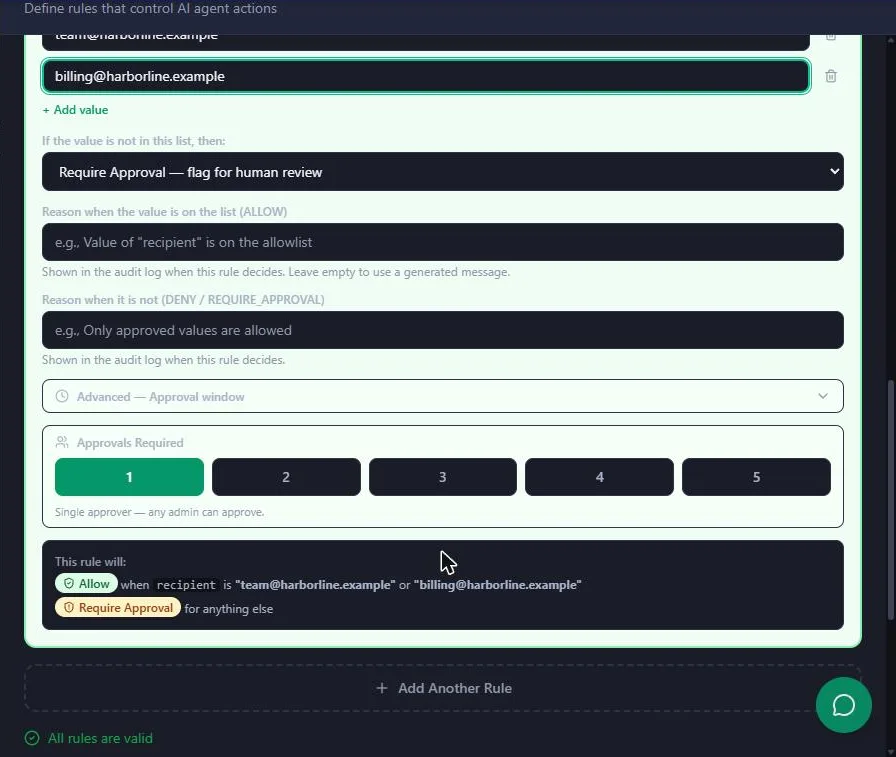
The goal of the setup is simple: team emails go out alone, client emails wait for a person, and deletes never run. That is human in the loop placed only where it matters.
What are the most common Guardian mistakes?
| # | Mistake | What happens | Fix |
|---|---|---|---|
| 1 | All three outputs wired to the send | Denied and held emails still go out | Connect Allowed only |
| 2 | Rule field name differs from the payload | The rule silently never fires | Test with the real payload |
| 3 | No project ticked | The policy won't save | Tick Default under Apply to Projects |
| 4 | An allow policy for deletes | Deletes can run | Rely on Deny unmatched actions |
| 5 | First test against a live send | A real email goes out mid-test | Disable the send or use Listen Mode |
| 6 | Two workflows listening for one action type | An approved email is sent twice | One active listener per action type |
| 7 | Action type typed differently in n8n | The node's request doesn't match the policy | Use the same email.send in both |
| 8 | API key pasted into a chat or shared workflow | Anyone can act as your workflow | Keep it in the Guardian API credential |
Why does the email still send when it needs approval?
1. Wiring every output to the send. The Guardian node has three outputs: Allowed, Denied and Needs Approval. Only Allowed connects to Send an Email. Denied and Needs Approval should each end in a note or a response. If all three feed the send, Guardian's answer makes no difference.
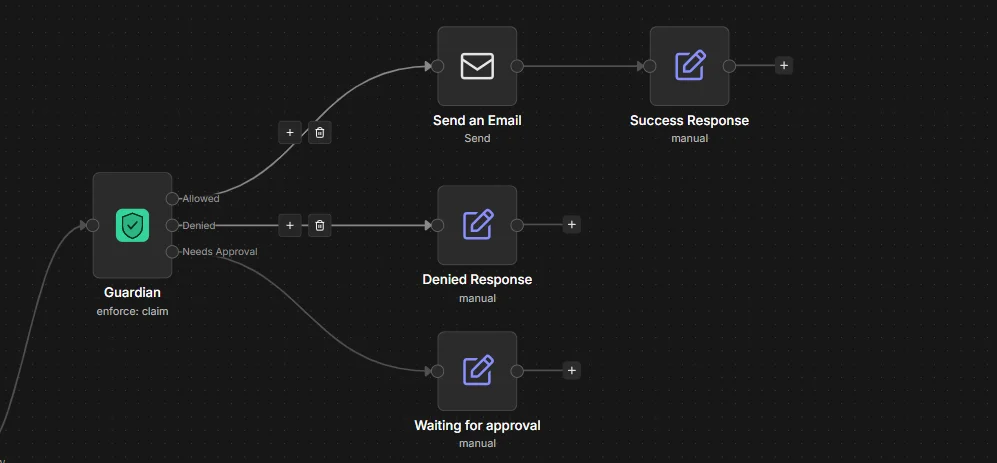
An approved email doesn't come back through that first node. It is sent by a separate approval path: a Guardian Approval Trigger, then a Guardian node set to Enforce, then the send, reading the approved payload.
Why does my Guardian rule never fire?
2. A field name typo. A rule checks a field by name. If the rule checks recipent and the workflow sends recipient, the rule is silently dead. The lesson's knowledge check asks exactly this. The fix is testing: Test This Policy before you save, and the flask icon on the saved policy afterwards. Run one payload that should pass (a team address returns ALLOW) and one that should not (a client address returns REQUIRE APPROVAL). Both are sandbox tests, so nothing is created or logged.
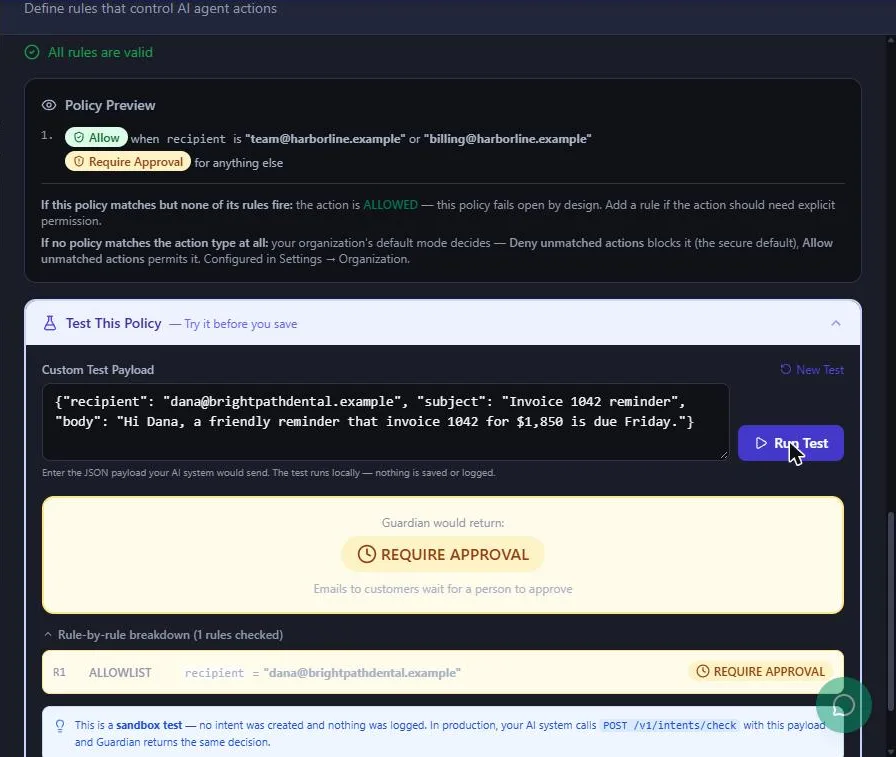
7. A different action type in n8n. The policy applies to one action type in lowercase dot notation, email.send. The Guardian node's Action Type must be the same string, and its payload must use the same field names as the rule: recipient, subject and body.
Why won't my policy save?
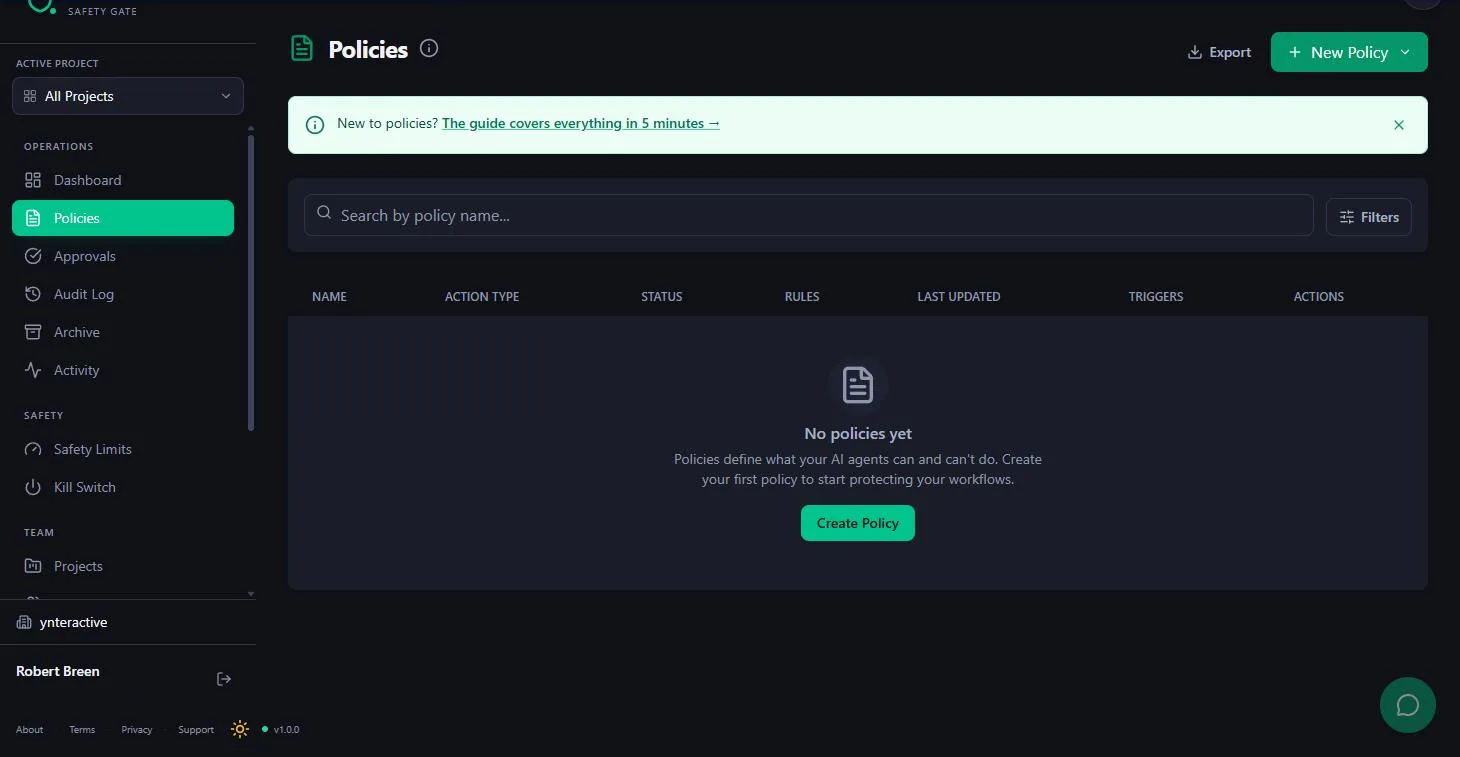
3. No project. Under Apply to Projects, tick Default. Guardian won't save a policy without a project. While you're on that form: the Manual option builds rules from scratch, and the AI Wizard isn't available yet, so use Manual and build the rules by hand.
Try it free, step by step
Guardian: Make Your n8n AI Agent Ask Before It Emails a Customer. A business case for a small firm whose n8n agent drafts client emails: turn "team emails go out alone, client emails wait for a person, deletes never happen" into a Guardian policy, test it, and see… You do every step yourself in a practice copy of Guardian, it checks your work as you go, and “Do it for me” finishes any step you get stuck on. Free, and nothing touches your real accounts.
Start the free lessonHow do I stop an agent from deleting records?
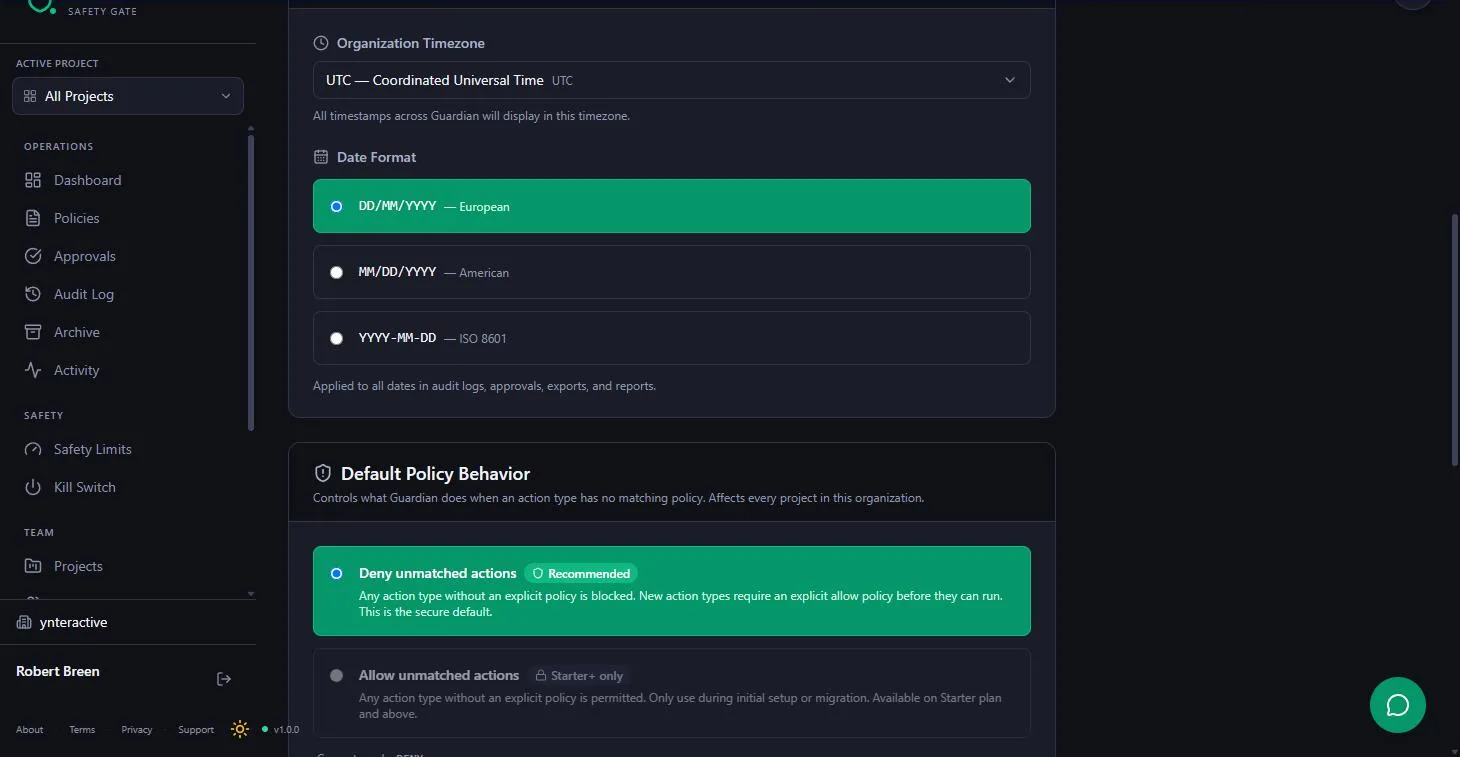
4. Writing an allow policy for deletes. You don't need a "never delete" rule at all. Under Settings > Organization, Default Policy Behavior has Deny unmatched actions selected and marked Recommended: any action type without an explicit policy is blocked. If the agent ever asks for record.delete, Guardian answers Denied. The only way to break that is to write an allow policy for it, so don't. (Allow unmatched actions is the wrong default for this job anyway.) This is how a policy engine limits agent permissions: the safe answer is the default one.
How do I test without sending a real email?
5. Testing against a live send step. For the first real run, disable the send node (select it and press D), or turn on Listen Mode under the Organization tab. Listen Mode records every request and what Guardian would have decided, without blocking anything. Read those decisions, then switch it off.
Why did an approved email go out twice?
6. Two listeners. If two active workflows listen for the same action type, both can act on one approval. Keep exactly one active workflow listening for email.send. If you copy a workflow to experiment, deactivate the copy.
Where should the Guardian API key go?
8. Anywhere but the credential. Create the key under Settings > API Keys (Guardian asks you to verify your email first) and add it, with the signing secret and the base URL, to the Guardian API credential in n8n. Don't paste it into a chat, a screenshot or a shared workflow.
What does a working setup look like?
A client reminder arrives in the Approval Inbox marked "Blocked, awaiting human approval" with the reason and an expiry time. Edit Payload & Approve shows the original payload next to the one that will run, so you can fix a wrong amount first. The original stays in the audit trail, and the edited version is checked against the policy again. For all settings on one page, use the Guardian cheat sheet; for the tool listing, see Guardian in the AI tools directory.
Key takeaways
- Wire only Allowed to the send; approvals use their own trigger path.
- Test every policy with the real payload, before and after saving.
- Leave Deny unmatched actions on and never allow deletes.
- Use Listen Mode or a disabled send for the first run.
- One active listener per action type, and the key stays in the credential.
Frequently asked questions
- Does Guardian send the email for me?
No. Guardian only answers Allowed, Needs approval or Denied and records the decision. n8n does the sending.
- What does Guardian return for an email to my own team?
With the lesson's rule, ALLOW, because the address is on the list. Everything else gets REQUIRE APPROVAL.
- Can I change a draft before approving it?
Yes, with Edit Payload & Approve. The edited version is checked against the policy again.
- How many approvals does one email need?
The lesson leaves Approvals Required at 1.
- Where can I read more answers?
See the Guardian for n8n FAQ and Guardian use cases by role.