What is a SOC 2 report?
Quick answer
A SOC 2 report is an attestation report from an independent CPA firm, under standards set by the AICPA, describing a service company's controls over areas such as security, availability, processing integrity, confidentiality and privacy. Customers ask for it to judge whether a vendor can be trusted with their data.
Last updated
Updated · By Robert Breen
Why it matters for a small business
When a vendor says "we take security seriously," you have no way to check. A SOC 2 report gives you an outside auditor's view instead. It comes in two kinds. A Type I report looks at whether controls are suitably designed at a single point in time. A Type II report also tests whether those controls actually operated effectively over a period of months, which is why buyers usually prefer it.
The report is not a pass or fail certificate. It describes the system, lists the controls, and in a Type II shows what the auditor tested and any exceptions found. It also lists controls the customer is expected to handle, such as managing your own users. Vendors usually share the full report only under a non-disclosure agreement, and some publish a shorter, public SOC 3 summary.
In a real lesson: Reply Faster to a Client Asking for a Case Update: ChatGPT for Small Law Firms
In the Reply Faster: Client Case Updates lesson, Owen Park, a paralegal at Harbor Street Law, a made-up firm, answers a worried client. One of the firm's facts says it does not accept evidence by text, so the client should "upload the screenshots to the secure client portal under Documents."
That one line is why vendor reviews matter. The portal is run by software the firm relies on to hold client evidence safely, and the inbox even shows an Office Admin note that the portal "will be down Saturday from 8 to 10 a.m. for updates." The lesson does not cover how the firm chose that portal. In real life, asking the vendor for its SOC 2 Type II report, and reading the exceptions, is a normal part of that choice.
The lesson's main habit applies too. Owen checks every claim against facts before sending. Treat a vendor's security claims the same way: match each promise in the sales deck to something in the report.
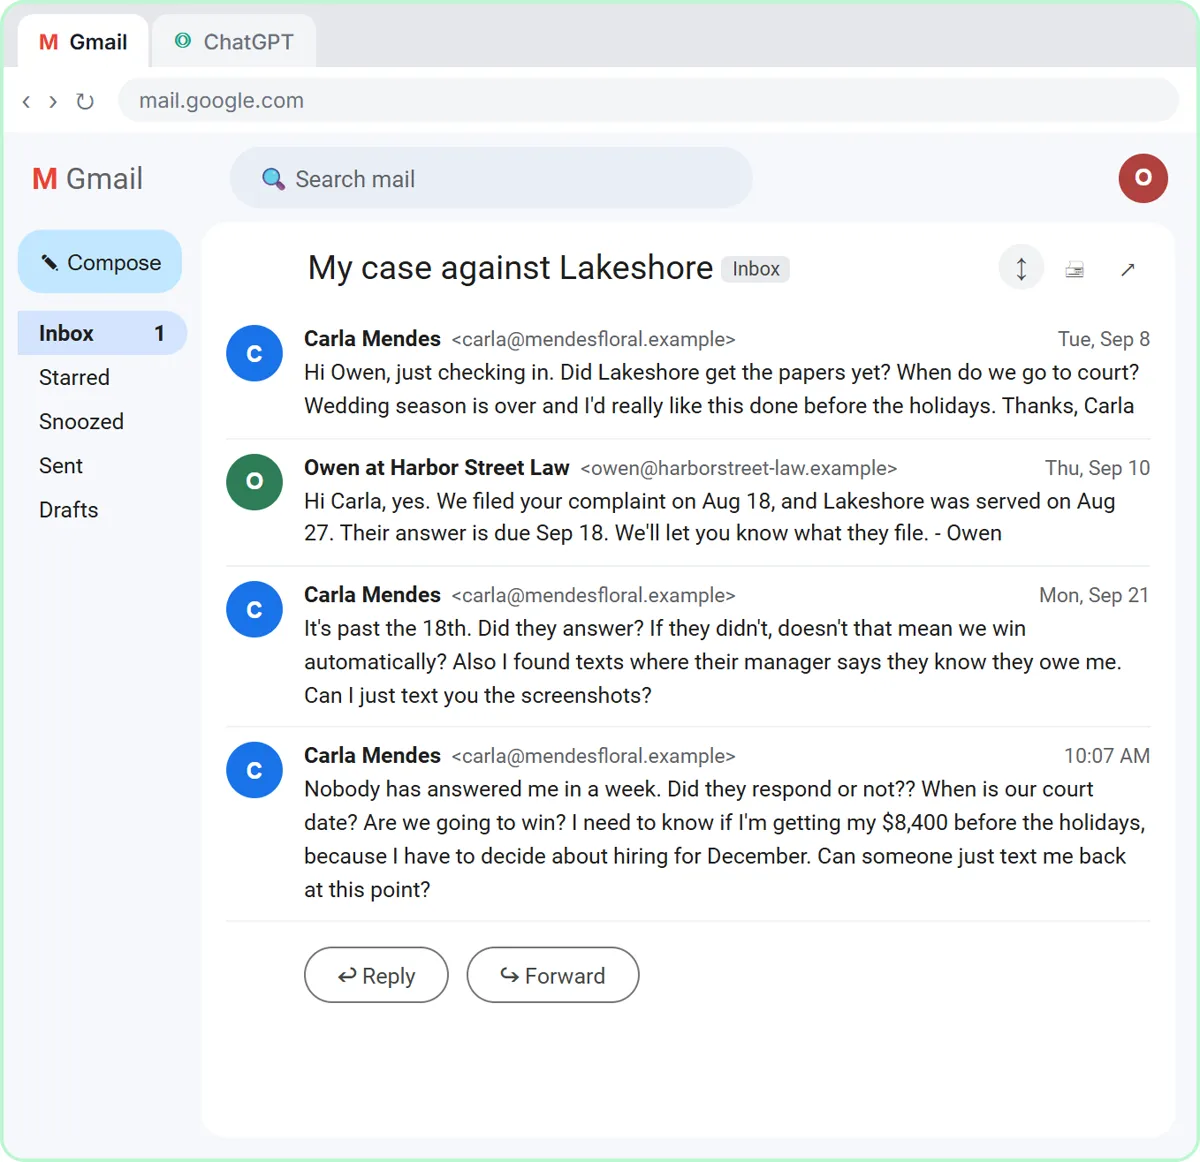
Try this lesson free or read the step-by-step guide.
Common confusions
SOC 2 vs ISO 27001
Both are common ways vendors show security practices. SOC 2 is an attestation report by a CPA firm under AICPA standards. ISO/IEC 27001 is an international standard a company can be certified against. Neither one guarantees a vendor will never have an incident.
SOC 2 vs SOC 1
SOC 1 reports focus on controls relevant to a customer's financial reporting, which matters to auditors. SOC 2 focuses on security and related areas, which matters to anyone trusting a vendor with data.
Tips
- Check the dates. A Type II covers a specific period, so ask how recent it is and whether a bridge letter covers the gap since.
- Read the exceptions and the vendor's responses, not just the opinion letter.
- Find the customer responsibilities section and make sure someone at your company owns each one.
- Confirm the report covers the product you are buying, not just another part of the company.
Related terms
More Business terms
Where you use it: free lessons
- Reply Faster to a Client Asking for a Case Update: ChatGPT for Small Law Firms (ChatGPT, 10 min)
- Reply Faster to Clients Chasing Their Refund: ChatGPT for Tax and Bookkeeping Firms (ChatGPT, 10 min)
Prompt templates that use it
Frequently asked questions
- Is SOC 2 a certification?
- Not exactly. It is an attestation report: an independent CPA firm gives an opinion on the vendor's controls. People often say "SOC 2 certified," but the accurate phrase is that the vendor has a SOC 2 report, ideally Type II.
- Does a small business need its own SOC 2 report?
- Usually only if larger customers ask for one before buying from you. Most small businesses deal with SOC 2 as buyers, asking vendors for theirs, rather than as companies being audited.